Dayonai
Secure virtual workstations on AWS, fully defined in Terraform. Adding someone to Google Workspace gives them a locked-down machine and the right AWS permissions for their role, automatically, all inside a private VPC with keyless OIDC deployments.
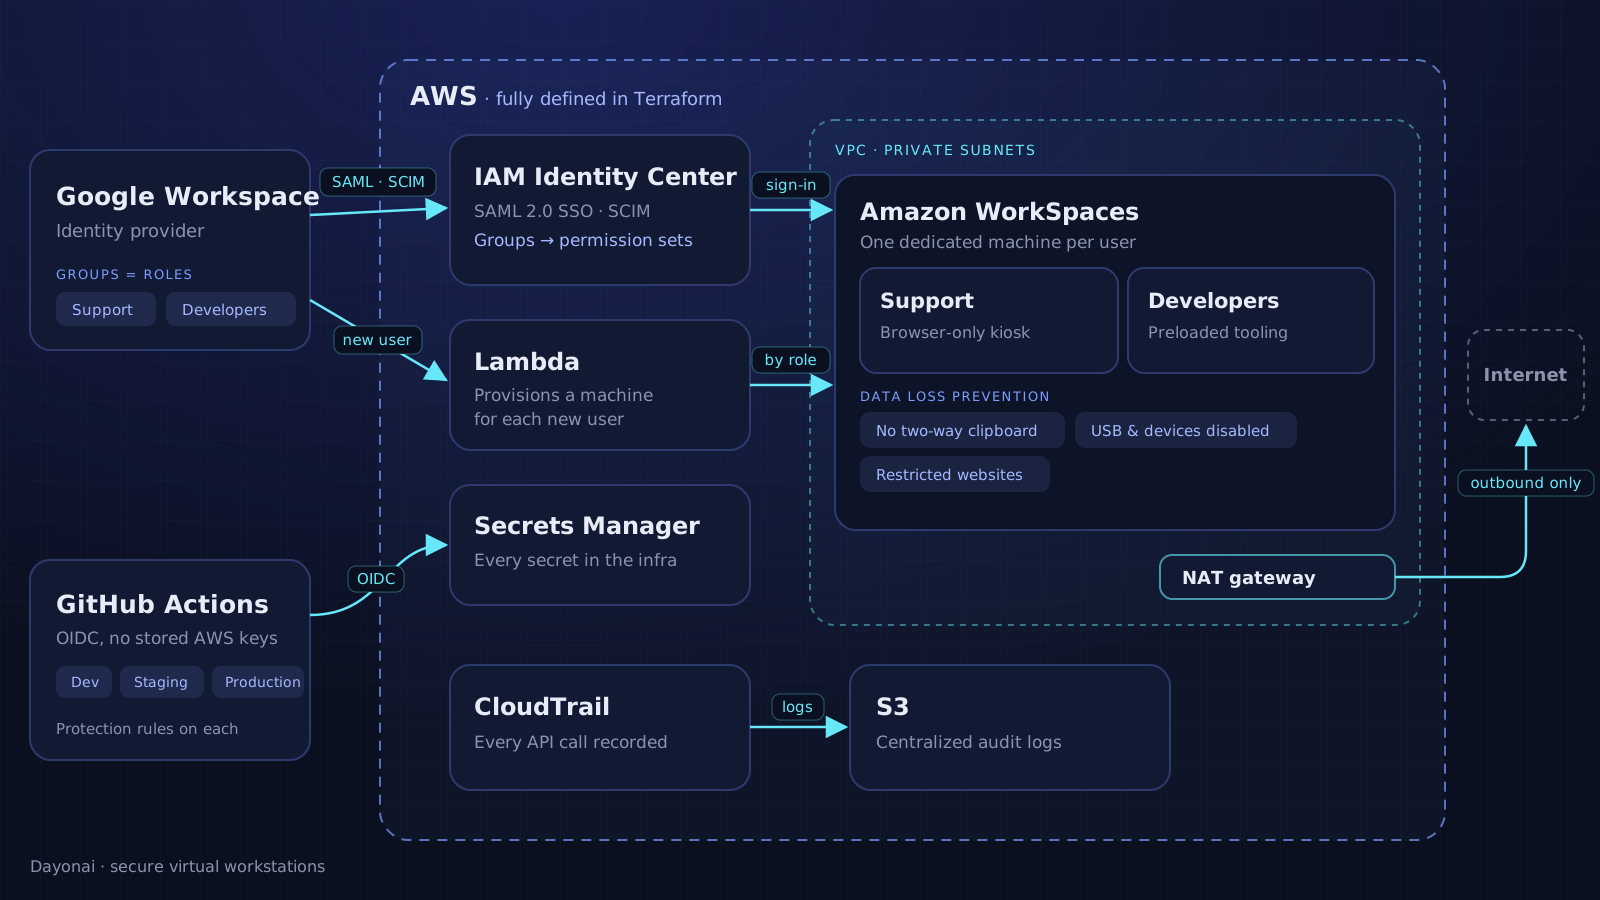
Overview
A secure virtual workstation platform for a client, architected on AWS and defined fully in Terraform.
Identity and provisioning
Google Workspace is the identity provider, connected through IAM Identity Center with SAML 2.0 single sign-on and SCIM.
Access follows the role. Each role is a Google group mapped to an AWS permission set. When someone’s Google profile is created and added to a group, SCIM syncs them into IAM Identity Center and they automatically get that group’s permissions in the AWS console. Nobody hands out AWS access by hand.
Provisioning is automatic. When a user is created in Google Workspace, a Lambda function launches a dedicated Amazon WorkSpaces machine with a role-based profile:
- Support staff get a browser-only kiosk
- Developers get a machine with their tooling preloaded
Network
I configured the VPC so nothing sits openly on the internet. Workloads run in private subnets, and NAT gateways give them outbound access without opening any inbound path.
Data loss prevention
- Two-way clipboard transfer is blocked
- USB and external devices are disabled
- Website access is restricted
Audit logging
CloudTrail and S3 provide centralized audit logging across the platform.
CI/CD and environments
I set up the delivery pipeline in GitHub Actions, with Dev, Staging, and Production kept apart as separate environments behind protection rules.
- No stored cloud keys: GitHub authenticates to AWS through OIDC, so the pipeline never holds long-lived credentials
- Secrets in one place: every secret for the whole infrastructure lives in AWS Secrets Manager, never in the repo or the pipeline
No Hesi →
The platform behind No Hesi's modded Assetto Corsa servers and its 200K+ member racing community. I led it through two migrations and built its desktop launcher, in-game chat overlay, league badges, and Discord-synced subscriptions.